find. prioritize. exploit. fix

Autonomous
Continuous Attack

AI-powered continuous pentesting with built-in triage to cut
through noise and focus on what matters.

Trusted by industry leaders worldwide
our Solutions

Unleash the power of security without limits

Optimize vulnerability management, streamline pentest reporting, and integrate DevSecOps into your workflows with Faraday.

Red Team. Pentesting. Research

Offensive security experts who think and attack like real adversaries. We find attack paths, exploit, validate and generate evidence to defend better.
Faraday Platform

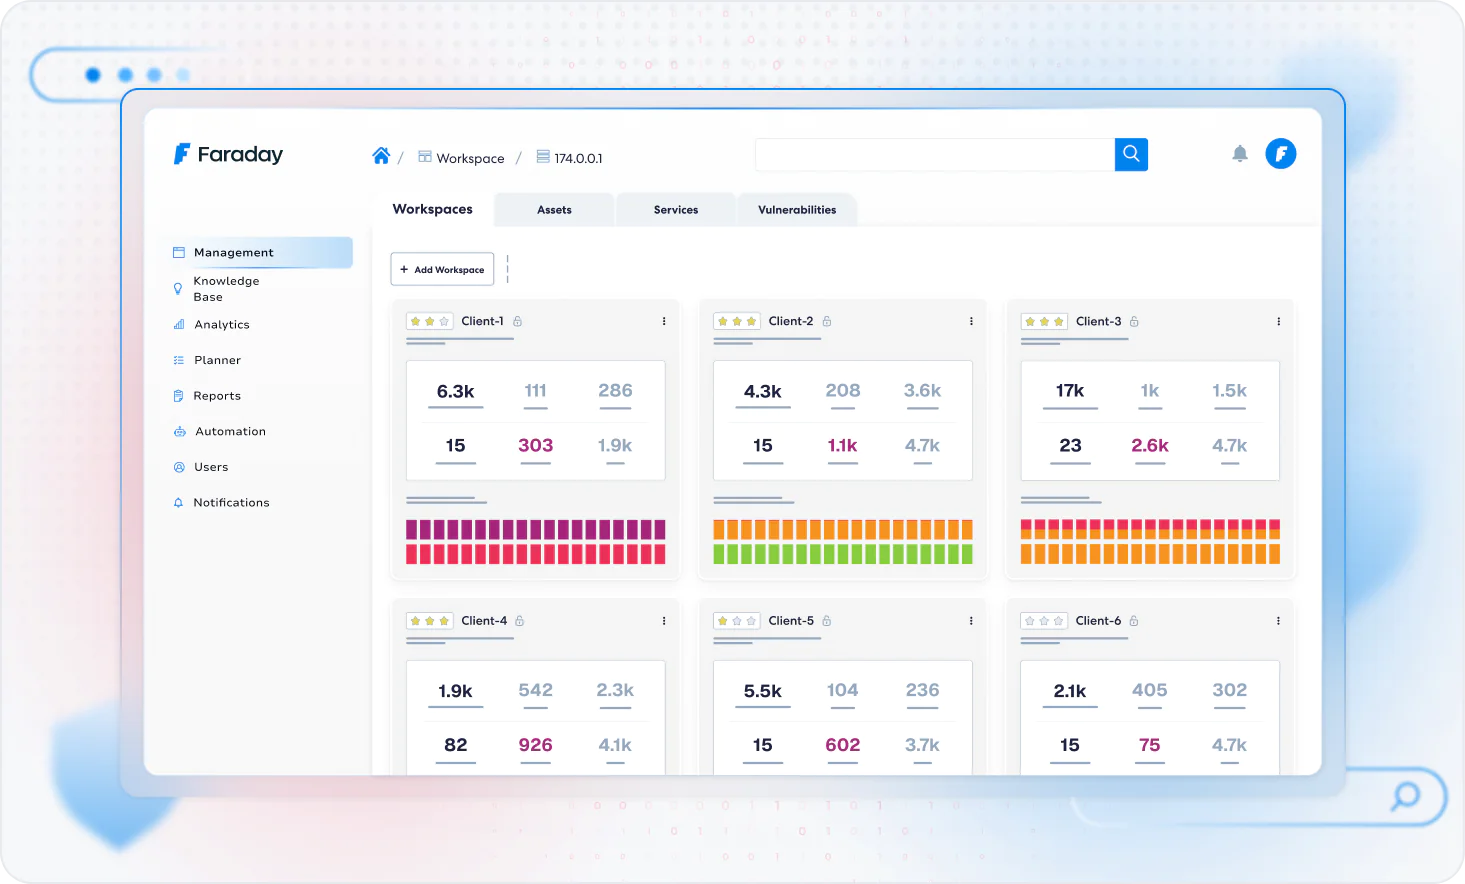
All the context. One view of risk. We connect vulnerabilities, tools and data to understand what is truly exposed, what can be exploited and where to act first.
Powered by FaradAI

AI applied to offensive security: simulates attacks, chains vulnerabilities and continuously explores new exploitation paths. Built for offensive security. Thinks like an attacker. Operates at scale.

Platform

One platform for every stage of offensive security

Platform, AI and expertise working as one. That is what makes autonomous offensive security possible.

FaradAI | The AI layer across every module

Triage · deduplicate · prioritize · explain · remediate · report

We simulate how they attack. Not how they scan.

We simulate how they attack. Not how they scan.

Chained autonomous attacks, not isolated vulnerabilities.

We connect findings to understand how far an attacker could go and what represents real risk.

Designed like a Red Team. Executed at scale.

AI executes, connects and accelerates. Human expertise brings context, judgment and control.

faradai

AI that attacks your environment 24/7. A human in control, always.

FaradAI runs continuous attack rounds across web, API, infrastructure and cloud, with a Faraday pentester supervising every cycle. Add intelligence modules and expert review as your program matures.

Human in the loop A Faraday pentester oversees the entire cycle, validates critical findings and can step in at any time.
Always on
01
Setup
Targetapp.client.com
ScopeWeb · APIs · Cloud
RulesWindows and exclusions
ScheduleRecurring, hands-off
AI-built attack plan, editable before launch
02
AI Pentest
52findings detected
9.8SQL Injection · /v2/transfers
8.4JWT token without expiration
8.1Reflected XSS · multipleDUP
7.6CORS wildcard · public API
5.3Exposed server version
3.1Soft 404 leak · /api/internalFP
2.9Banner grabbing
03
Triage + Patching
  • Classifies by CVSSScore · business context · real exposure
  • Automatic deduplication14 duplicates removed
  • Validates false positives9 false positives removed
  • Builds the patch planBy type · ready or needs action
29real findings to review
04
Output
PlatformReportsTicketingMCP
Faraday Platform AIAsk your workspace
Which hosts have critical vulnerabilities?
Four: 10.0.4.12, 10.0.4.30, 10.0.7.8 and db-prod-02.
Open Jira tickets for the critical ones.
Done: I opened 11 issues, one for each critical finding.
↻ Continuous cycle: when one round ends, the next one begins
Continuous Attack Rounds
24/7 0
Surfaces: Web, API, Infra, Cloud
0
Criticals Validated by a Human
0 %
From Kickoff to First Findings
+ 0
Offensive Security at the cORE

Get work done with your security assistant

Introducing your security agent. Ask your Faraday workspace anything in plain language. The agent answers with your real data and acts on it, while every critical decision stays with your team.

Faraday Platform AI
Ask your workspace
Online
Ask a question…
Integrations

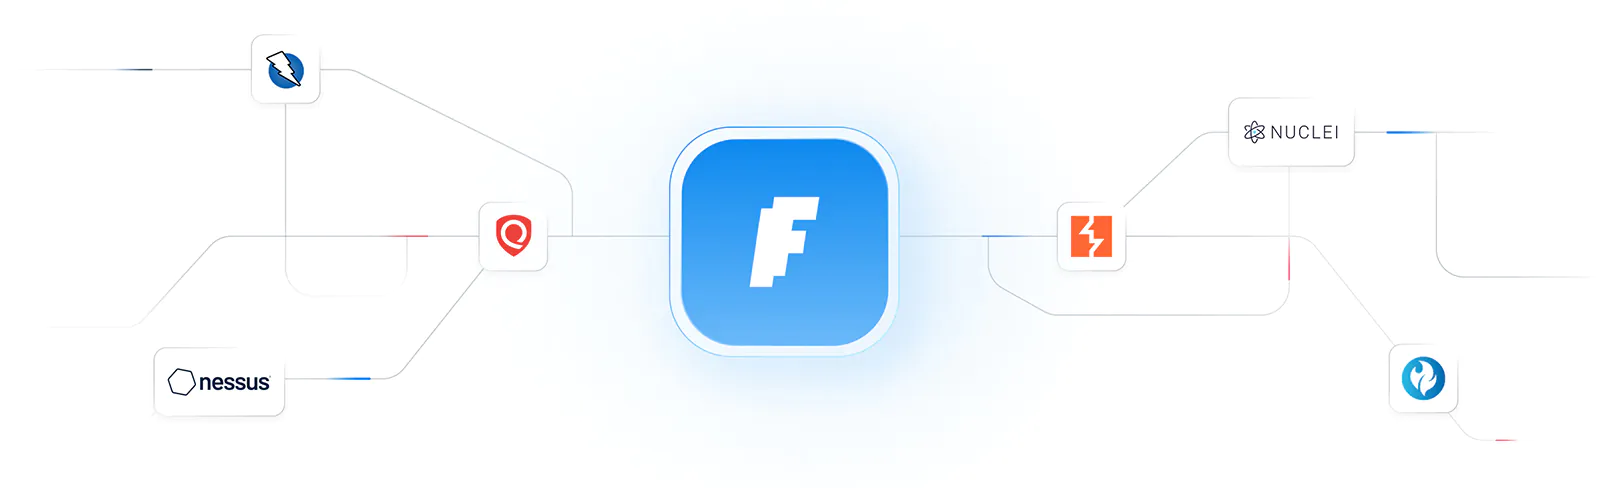
Seamlessly integrated with your security and IT ecosystem

Showcase popular tools and platforms compatible with Faraday
24/7 Protection with Live Reporting

Start your security journey with us

Whether you’re exploring modular coverage or need expert validation, we’re ready to assist.
Tell us what you’re looking for — our team will respond shortly.